Thank you
The email was sent through mg.foundation.xyz, using IP address 159.112.252.180, which is associated with Mailgun’s email-delivery infrastructure. The DKIM signature was authenticated for foundation.xyz. it indicates the message traveled through email infrastructure authorized to send on behalf of Foundation’s domain. However, successful authentication does not establish that Foundation authorized the message. Someone could potentially have obtained unauthorized access to its mailing system or sending credentials.
They have our phone numbers…
They do.
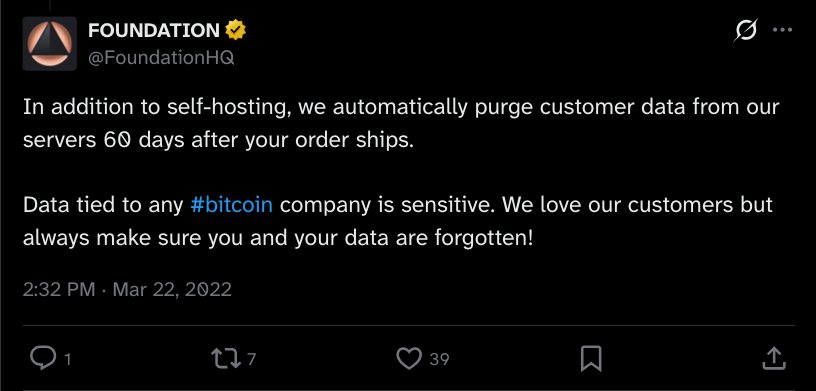
Wonder how they’re going to justify
Doubt they will justify it. They will admit how and what happened and apologize for the breach of customer trust, just the same way the other HWW vendors did (Ledger, Trezor, Bitbox, Keystone…)
Yes. Everything about you. Order, name, address, email, phone number, even the method of shipment.
Does anyone know how long Foundation keep your personal details, like delivery address for? in my email it didn’t show the delivery address. Wondering if that is only for recent purchases that have been breached?
To play the devil’s advocate, the breach might have been some time ago and the data kept for this moment.
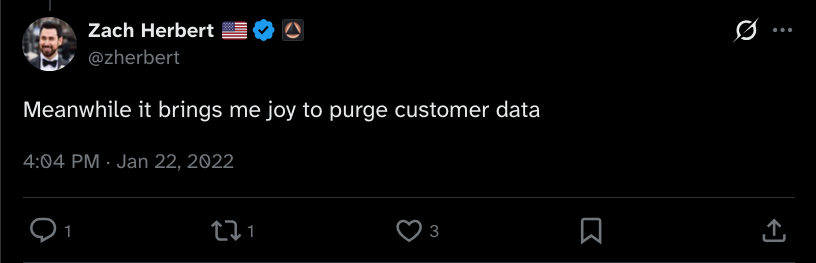
I’m so disappointed in Zach and his team right now. My residential address, phone number, email address, everything is out there. My delivery was almost a year ago, and they kept all this data around, possibly even on MAILGUN, of all places. All the while lying about deleting the data out of “love” for their customers.
Luckily I’ve since moved houses, and used a disposable email address, but I guess I’ll have to live with scam phone calls now, and I may have to warn the new residents at my old address that they might get scary visitors.
Not Good and Not Happy ! 
Just in case anyone misses the official incident updates, they are being posted in this thread.
Thank you for the update. The one on Reddit is helpful too. I appreciate your transparency. But I struggle to understand how a Cloudflare API key could somehow give an attacker this level of access. I almost wonder if it was an inside job.
This was not an inside job. There will be a full report later this week.